Privacy
12 articles tagged “Privacy”. Tags cut across categories, so you may find analytics, chat and product notes side by side.
Tagged Privacy
12 articles
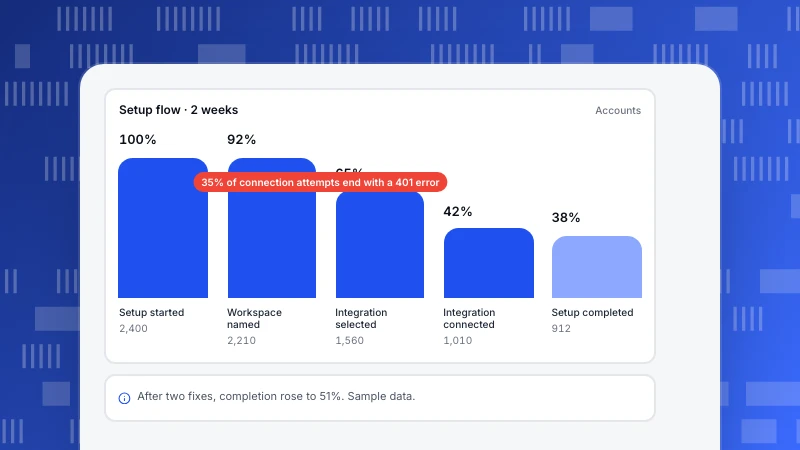
User behavior tracking: what to track, methods and privacy
What user behavior tracking is, which behaviors to track, six tracking methods compared, how to set it up with privacy in mind, and a setup-flow example.
Read more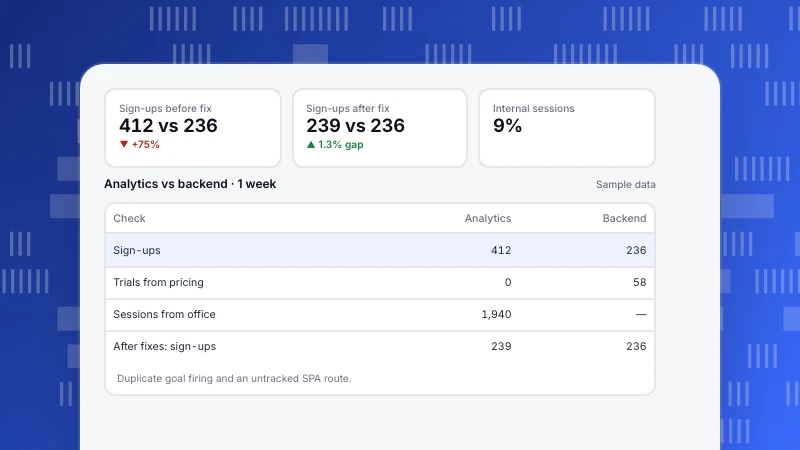
Implementing web analytics: an 8-step plan and checklist
How to implement web analytics properly: questions, tracking plan, installation, events and goals, data hygiene, privacy and verification against your backend, with a worked example.
Read more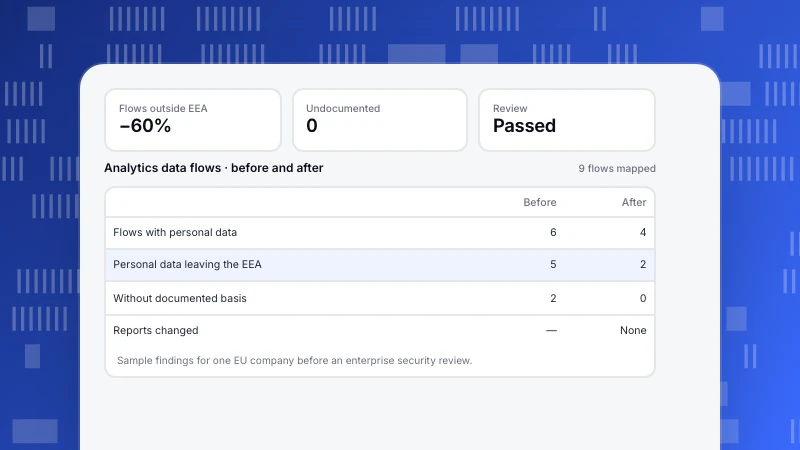
Data residency: what it means, the laws, and how to map your analytics data
Data residency is where your data is physically stored. How it differs from sovereignty and localization, the main laws (GDPR, PIPL and others), why analytics is affected, and a worked mapping of nine data flows.
Read more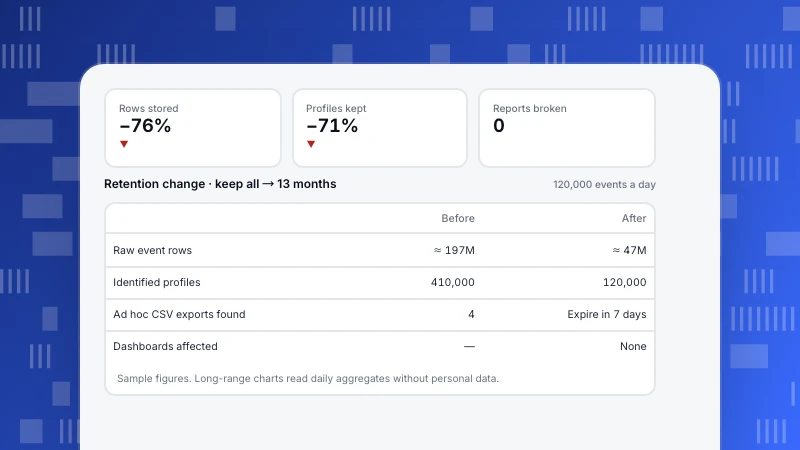
Data retention policy: legal basis, a sample schedule and how to enforce it
A data retention policy sets how long each type of data is kept and how it is deleted. The legal basis (GDPR, CCPA), what to include, a sample schedule for analytics data, and a worked example of moving from "keep everything" to 13 months.
Read more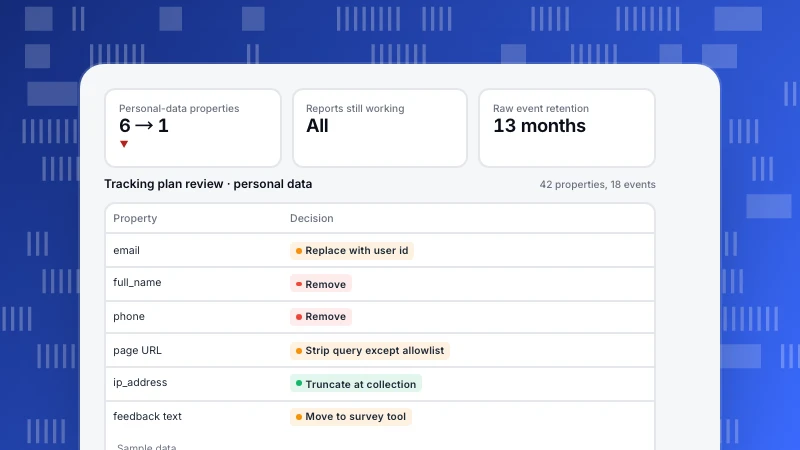
Privacy by design: the 7 principles, GDPR Article 25 and a worked example
Privacy by design builds privacy into products from the start. The seven principles translated into team practice, what GDPR Article 25 requires, a tracking-plan review that cut personal-data fields from six to one, and a checklist.
Read more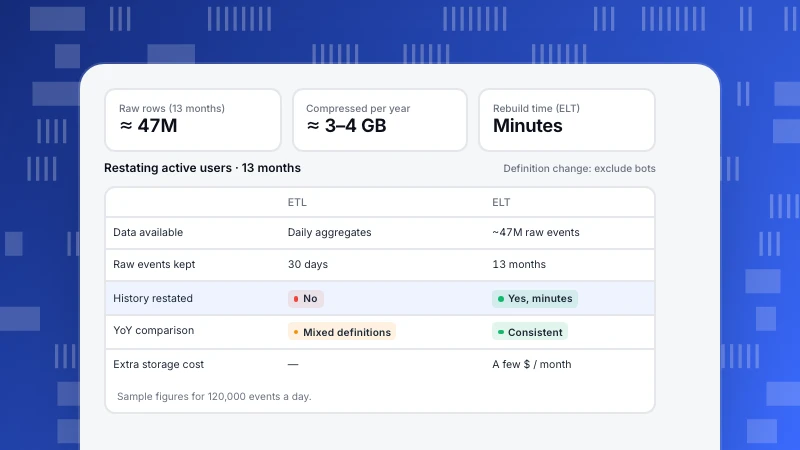
ETL vs ELT: differences, a worked example and how to choose
ETL transforms data before loading; ELT loads raw data and transforms it in the warehouse. A comparison table, a worked example of restating a metric after its definition changes, the privacy catch, EtLT, reverse ETL and a decision checklist.
Read more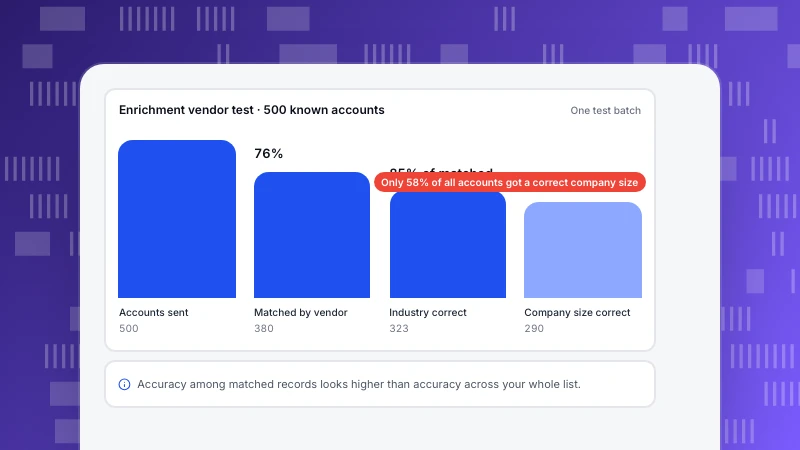
Third-Party Data: What It Is, When It Helps and How to Test It
Third-party data is collected by a company with no direct relationship to the people it describes, then sold or shared. How it differs from first- and second-party data, where it still helps, its risks, and how to test a vendor’s accuracy before you rely on it.
Read more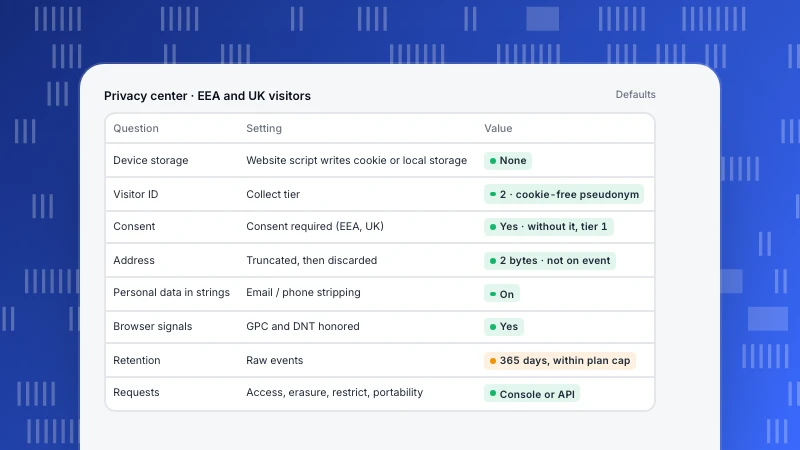
GDPR-Compliant Analytics: A Checklist for Choosing and Setting Up a Tool
No analytics tool is GDPR compliant by itself; compliance depends on what you collect and how you set it up. A checklist of what to check in any tool, tied to the regulation text, with the matching settings in TapCub.
Read more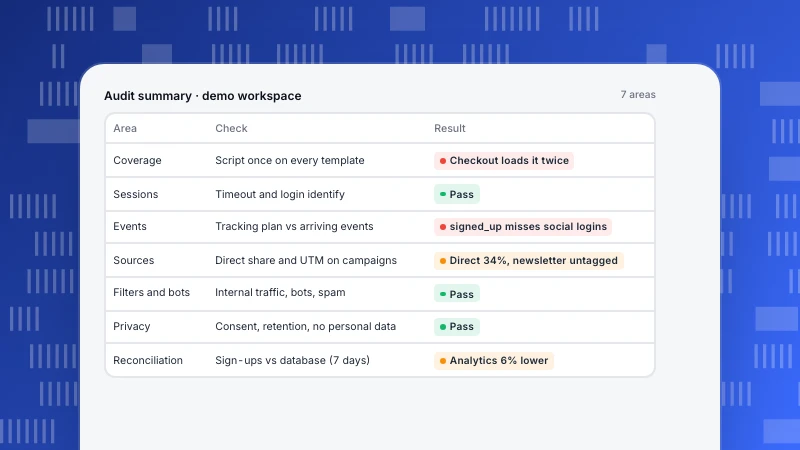
Web Analytics Audit: A Checklist in Seven Areas
A web analytics audit in seven areas: coverage, sessions and identity, events, sources, filters and bots, privacy, and reconciliation with your backend. A concrete check for each, how to run it, and how to keep it healthy afterwards.
Read more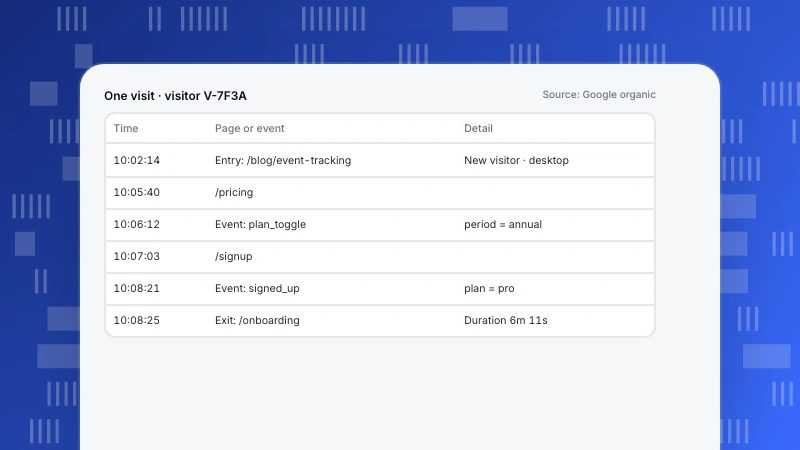
Website Visitor Tracking: Four Layers and What Each Can See
Website visitor tracking in four layers: aggregate counts, sessions and paths, identified users after login, and company identification. What each layer sees, what it needs, and where privacy changes what you should collect.
Read more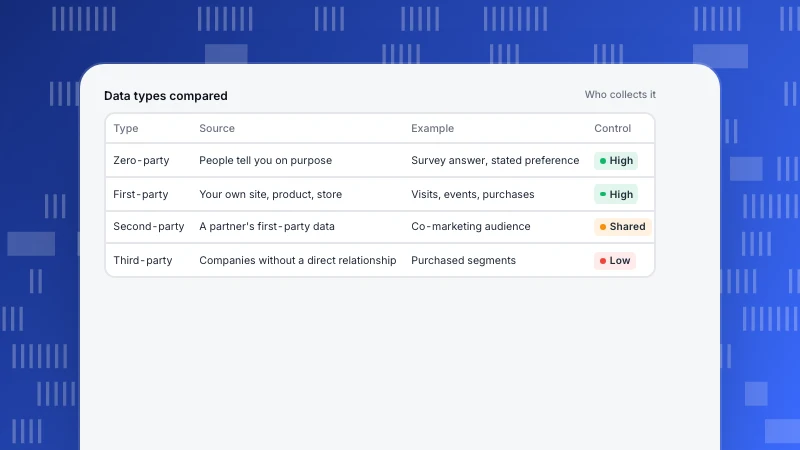
First-Party Data Strategy: Collect for Decisions, Keep Less
A practical first-party data strategy: what counts as zero-, first-, second- and third-party data, how to plan collection around decisions, identity and consent choices, and minimisation and retention defaults.
Read more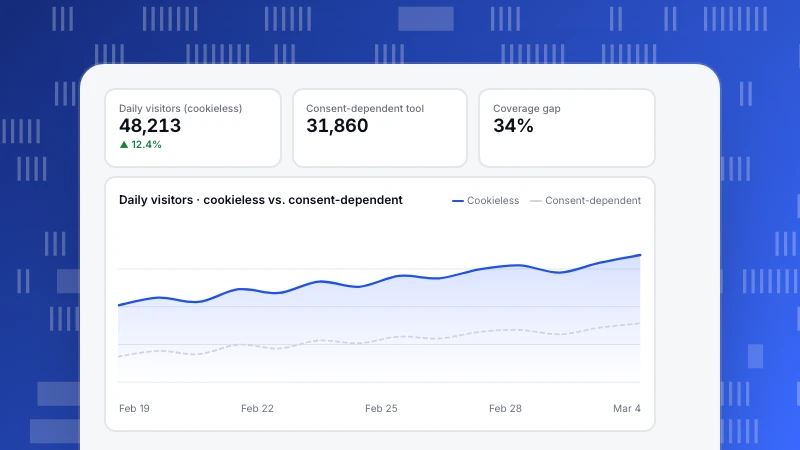
Cookieless vs cookie-based analytics: accuracy, consent and what changes
Cookieless vs cookie-based analytics compared: how each counts visitors, where each goes wrong, what the law says about consent, and what to check when you switch.
Read more