Try it on your own data
Every report in this article is in the free plan. One snippet for web and apps, up to 10 sites.
Start free"Cookieless" has become a label vendors attach to anything privacy-adjacent, and most comparisons are written by someone selling one side. This guide compares cookieless and cookie-based analytics on the things that matter: how each counts a visitor, where each one's numbers go wrong, what you lose and gain, what EU guidance actually says about consent, and what to check when you switch.
What you will learn
- Cookieless counts more completely day to day; cookies follow an anonymous person further
- The two models make opposite errors, so compare daily visitors, not monthly
- Not writing to the device removes the usual consent trigger, but check your regions
What changed · Nov 3, 2026
Rewritten as a cookieless vs cookie-based comparison: error sources, consent rules with EDPB guidance and a switching checklist.
Cookieless vs cookie-based analytics: the short answerHow a cookieless visitor is countedAccuracy: where each model goes wrongMeasure the gap on your own siteWhat you give upConsent and the lawCookie vs. cookieless, side by sideWhen you still want identitySwitching: what to checkFAQ
Cookieless vs cookie-based analytics: the short answer
New section
The difference between cookieless vs cookie-based analytics is where the visitor identifier lives. Cookie-based analytics writes an identifier into the browser and reads it back on every visit. Cookieless analytics writes nothing to the device; it tells visitors apart on the server, from information that arrives with every request anyway. That one choice changes three things: how many visitors you see, how well you can follow the same person over time, and what consent you need.
"Cookieless" is also a label vendors attach to anything privacy-adjacent, so it is worth being precise. In TapCub it means the website script writes neither a cookie nor local storage, visitors are counted from a keyed hash computed on the server, and it does not fingerprint: it does not read fonts, canvas rendering or screen details to build an identifier that follows people across networks.
How a cookieless visitor is counted
New section
On each request the collector combines the site, a secret salt, the truncated IP address and the browser type, runs a keyed hash and keeps only the result. The inputs are discarded. Two requests from the same browser on the same network produce the same hash and count as one visitor.
What happens the next day depends on the privacy preset. Balanced, the default, keeps a site-level salt, so new and returning visitors can be compared. Strict rotates the salt each day and does not report returning visitors across days. Both truncate the address before storage (counting modes and privacy presets). In pseudocode:
// balanced (default): one salt per site, kept
// strict: a new salt every day, old ones expire
salt = strict ? dailySalt(site, today) : siteSalt(site)

// inputs arrive with every request anyway
visitorId = hmac(secret, salt + site + ip + browserType(userAgent))

// keep the hash, discard the inputs
store(event, visitorId)
forget(ip, userAgent)
Accuracy: where each model goes wrong
New section
Neither model is "accurate" in general. Each has known error sources, and they point in opposite directions:
| Error source | Cookie-based | Cookieless (server-side hash) |
|---|---|---|
| Visitor declines consent | Not counted at all | Counted |
| Ad blocker or privacy browser blocks storage | Often not counted, or a new visitor each time | Counted, if the script runs |
| Browser shortens cookie lifetime | Returning visitors look new after the cap | Not affected |
| Same person on a new network or browser | Same visitor while the cookie survives | A new visitor |
| Several people behind one IP with the same browser type | Separate visitors | May merge into one |
| Same person across devices | Separate visitors unless logged in | Separate visitors unless logged in |
The browser row is not hypothetical. Safari's Intelligent Tracking Prevention caps cookies set by script to seven days (WebKit, ITP 2.1), so a cookie-based tool sees a weekly reader on Safari as a new visitor after a week away.
In practice, cookieless analytics gives you more complete daily counts, because declines and blocked storage do not remove anyone, and weaker long-range identity for anonymous visitors. Cookie-based analytics gives you better continuity for the people it can see, and sees fewer of them.
Measure the gap on your own site
New section
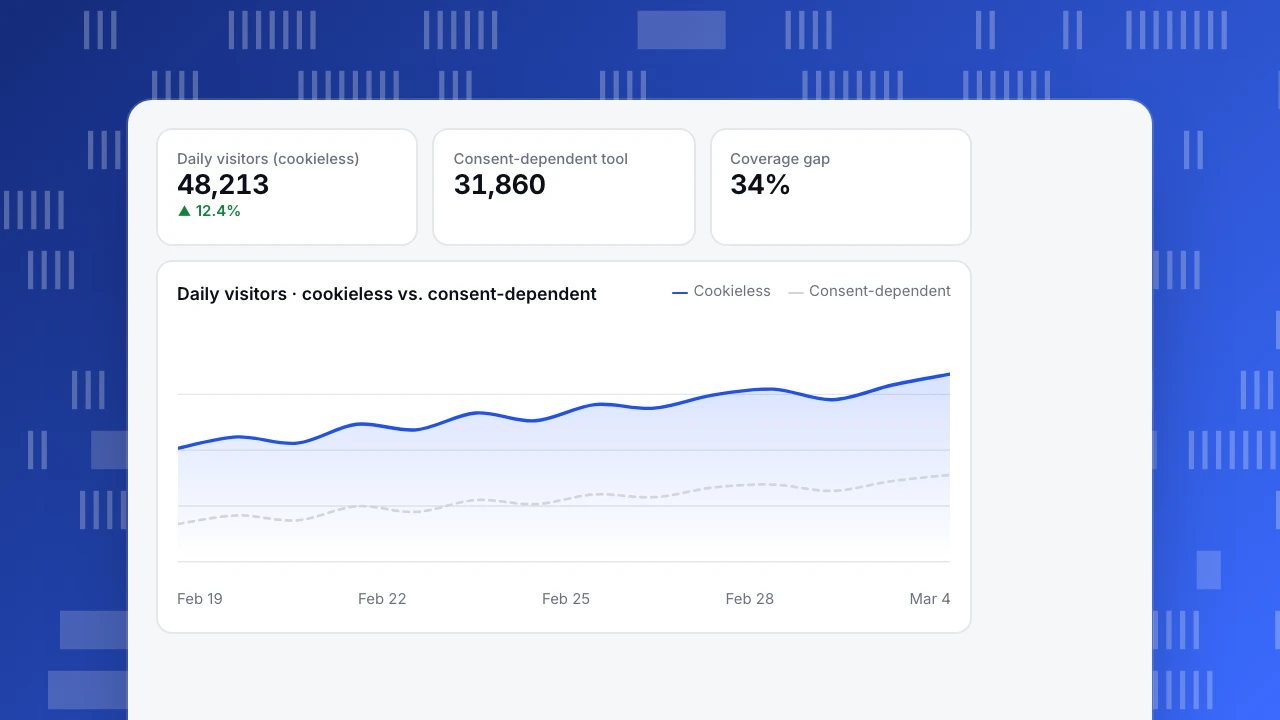
The size of the coverage gap depends on your audience, your regions and your consent banner, so measure it rather than borrowing a number. Run a consent-dependent tool and a cookieless tool side by side for two weeks on the same pages, compare daily visitors with bots excluded in both, and read the ratio by country. The sample below shows what the comparison looks like.
Daily visitors (cookieless)
48,213
▲ 12.4%
Consent-dependent tool
31,860
Coverage gap
34%
Daily visitors · cookieless vs. consent-dependent
CookielessConsent-dependentWhat you give up
New section
The honest trade-off is cross-day identity for anonymous visitors. In balanced mode, TapCub recognises a returning visitor as long as the browser and network stay the same; someone who reads on office Wi-Fi and again on mobile data counts twice. In strict mode nothing links across days: monthly uniques are effectively a sum of daily uniques, and "returning" exists only for identified users.
That changes a few reports:
- Monthly unique visitors run higher than in a cookie-based tool, slightly in balanced mode and noticeably in strict mode.
- New vs. returning for anonymous traffic is approximate in balanced mode and same-day only in strict mode.
- Attribution windows for anonymous visitors are shorter in practice, because a visitor who changes network is a new visitor.
- Ad platforms still need their own conversion data; cookieless site analytics does not replace an ad platform's conversion tracking.
Consent and the law
New section
In the EU and UK, the consent rule for devices comes from Article 5(3) of the ePrivacy Directive and its national versions: storing information on, or reading it from, a user's device generally needs consent unless it is strictly necessary. Analytics cookies usually fall under that rule, which is why the banner exists.
Not writing to the device removes the most common trigger, but it is not a blanket exemption. The European Data Protection Board's guidelines on the technical scope of Article 5(3) (final version adopted in 2024) look at techniques beyond cookies, including tracking based only on IP addresses, and conclude some of them can fall in scope (EDPB Guidelines 2/2023). Separately, an IP address is personal data under the GDPR, so processing it, even briefly, needs a legal basis and a mention in your privacy notice.
The practical position: cookieless measurement means that in many setups analytics no longer needs a cookie banner, but the decision belongs to you and your counsel for your regions. TapCub's privacy center can apply regional presets, including one that waits for consent before the script starts.
Cookie vs. cookieless, side by side
Section updated
The table summarises what each model can answer for anonymous visitors and for identified users.
| Question | Cookie-based | Cookieless (TapCub) |
|---|---|---|
| Daily unique visitors | Yes, minus those who decline | Yes, everyone |
| Monthly unique visitors | Yes (linked across days) | Balanced: linked while network and browser stay the same; strict: sum of daily uniques |
| New vs. returning (anonymous) | Yes | Balanced: yes; strict: within a day only |
| Retention for logged-in users | Yes | Yes, via identify() |
| Analytics consent banner | Required in most regions | Usually not required for analytics |
| Blocked by privacy settings | Often | No storage to block |
When you still want identity
Section updated
Cookieless measurement is the floor, not the ceiling. When a visitor logs in, your app can call identify() with a stable user ID, and from then on that person's events are attached to the ID across days and devices. Retention, lifetime value and user profiles are built on that. TapCub also has an identified mode that writes a device ID once consent is granted.
The rule we recommend: anonymous traffic is measured cookieless; identified users are measured by their account. It keeps the engineering simple too: one snippet, one identify() call at login, and no consent-mode logic deciding which events to drop.
Switching: what to check
Section updated
- Choose balanced or strict in site settings before you start comparing.
- Run both tools in parallel and compare daily visitors with bots excluded (why tools show different numbers).
- Update dashboards that quote monthly uniques or new-vs-returning, and add a note on the definition.
- Wire identify() into your login flow so retention for customers does not depend on the anonymous model.
- Review your consent banner and privacy notice for your regions with counsel.
The GA4 migration checklist covers the parallel run step by step.
FAQ
New section
Is cookieless analytics accurate?
It is more complete for daily counts, because visitors who decline cookies or block storage are still counted, and less precise for linking the same anonymous person across days, networks and devices.
Does cookieless analytics need a cookie banner?
Often not, because nothing is stored on or read from the device. EU guidance says some techniques without cookies can still need consent, and GDPR applies to IP processing, so confirm for your regions.
Why does cookieless analytics show more visitors than Google Analytics?
It counts people who decline consent or block storage, and treats a person on a new network or browser as a new visitor. Compare daily visitors with bots excluded to see the real coverage difference.
Can cookieless analytics track returning visitors?
In TapCub's balanced mode, yes, while the browser and network stay the same. In strict mode, returning visitors are not linked across days. Logged-in users are tracked by their user ID.
Is cookieless tracking the same as fingerprinting?
No. Fingerprinting builds a persistent identifier from device characteristics. TapCub's cookieless counting uses only the IP address and browser type that arrive with each request, keeps a hash and discards the inputs.
Update history1
- Major updateRewritten as a cookieless vs cookie-based comparison: error sources, consent rules with EDPB guidance and a switching checklist.
- First published
Was this article helpful?
We use your answers to fix and expand this page.
Couldn’t send. Please try again in a minute.
Thanks for the feedback. We’ll use it to improve this page.You’ve already sent feedback on this page. Thanks.

Data Engineer
Writes about event design, data quality, and collection workflows, with verifiable implementation methods for reliable analytics.